Your private network, as it should be.
Tartan is an always-on, encrypted overlay network. Your devices talk directly from anywhere. No VPN gateway. No subnet conflicts. A firewall on every device.
Control that goes past connecting.
- A passkey for every change. Every write needs a fresh passkey from an approved admin device. No passwords stored.
- Techs, just in time. A tech on your team gets a 10-hour certificate, signed off with their own passkey each time, and in the audit log.
- Partners get exactly what you grant. One port on one name, and nothing else. Revoke it and it’s gone in seconds.
- Every change on the record. Who, what, when, from which device.
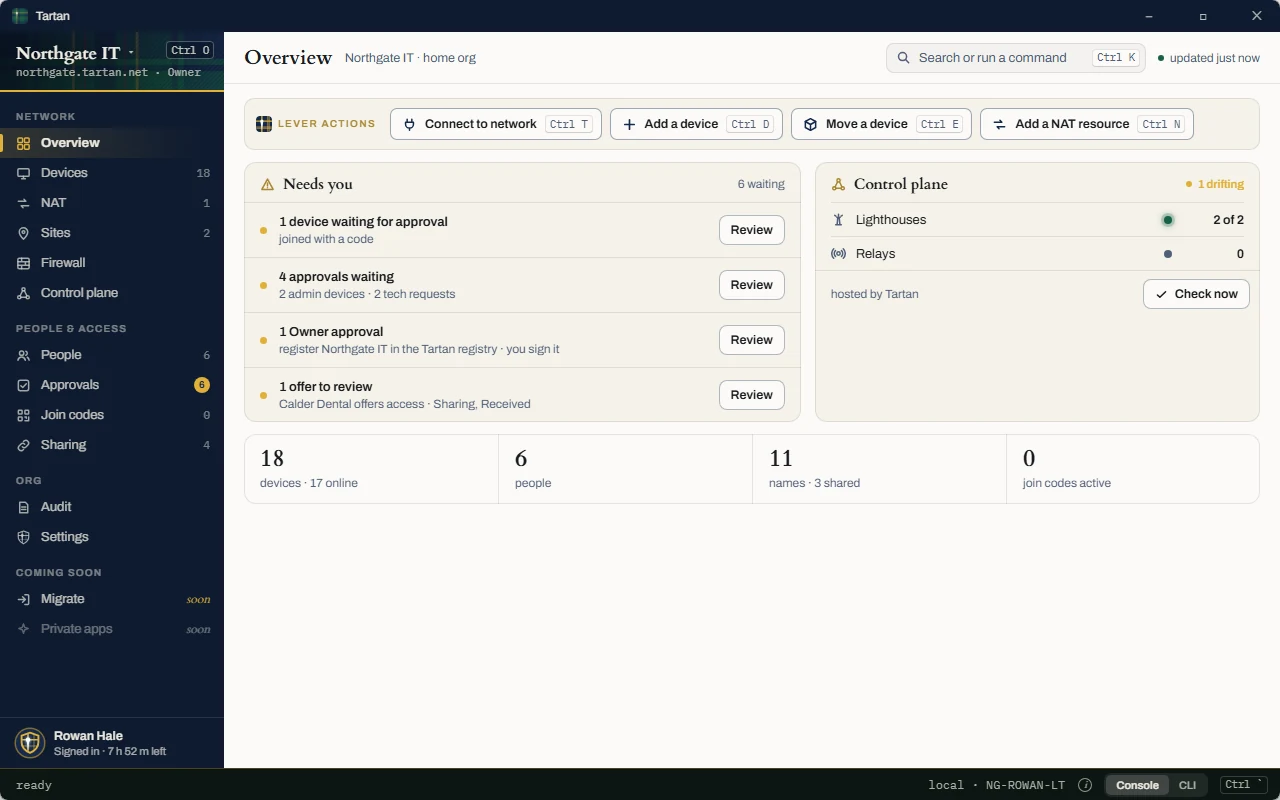
The network your org runs on.
Not a tunnel people open when they’re out. One private, encrypted network that every device is always on, wherever it sits.
Every site on one overlay.
Offices, homes and phones on one encrypted network. Two sites both on 192.168.1.0/24? Join them as they are.
Direct, device to device.
Peer to peer, straight through NAT. No VPN box in a closet to slow every packet or take everything down.
Always on.
The agent runs as a service: on your network from boot, before anyone signs in. Phones stay on too.
IPv6-first, without the headache.
Your org gets its own private IPv6 /48; every device gets an address as it joins. IPv4 LANs keep working through NAT64.
A name for everything.
files.acme.tartan.net, printer.acme.tartan.net. Real TLS certificates on private hosts.
A firewall on every device.
Default deny, checked by certificate, not IP. RDP to these, SSH to those, nothing else.
Beyond the VPN gateway.
What changes when the network is an overlay instead of a box.
| A VPN gateway | Tartan | |
|---|---|---|
| Where traffic goes | Through one gateway box | Device to device, direct |
| Joining sites | A tunnel per pair of sites; renumber when subnets collide | One overlay; conflicting subnets join as they are |
| When it’s on | When someone connects | Always, from boot, in the office or out |
| Addresses | Hand-planned IPv4 ranges | A unique IPv6 address per device, assigned for you, and a name for each |
| The firewall | At the edge of each site | On every device, default deny, by identity |
| Partners and techs | Shared VPN accounts | Grants down to one port that expire; a tech’s access lasts 10 hours |
Hold your own ground.
Your network. Your names. Your rules.
Public access is coming soon.
Want in early? Email us and we’ll set you up with the preview.
preview@tartannetworks.comEmail us